
While organizations fend off over 600,000 daily attacks, mismanaged credentials, excessive privileges, and inadequate disaster recovery leave corporate systems exposed
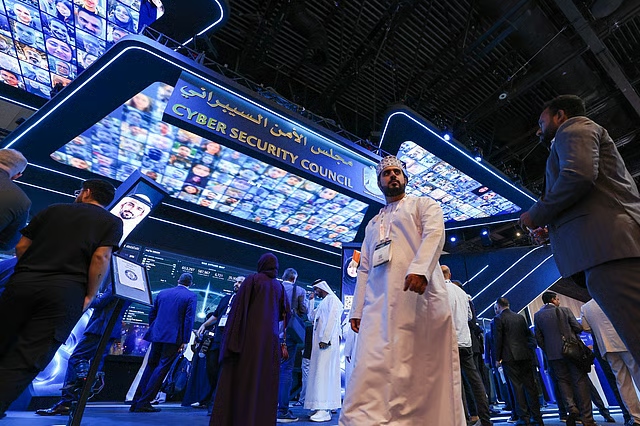
DUBAI, Sept. 18, 2026 : Corporate cybersecurity failures across the United Arab Emirates stem primarily from operational oversights, mismanaged access credentials, and flawed disaster recovery plans rather than firewall breakdowns or external artificial intelligence capabilities, industry executives warned as GISEC Global 2026 concluded in Dubai on Friday.
The warning coincides with data from the UAE Cyber Security Council showing the country repels more than 600,000 cyber intrusions every day—equivalent to roughly 416 attacks every second. A growing proportion of these intrusions are orchestrated or accelerated using artificial intelligence tools.
Yet regional defense experts speaking at the Dubai Exhibition Centre cautioned that internal enterprise posture remains the primary vulnerability. Findings from an IBM regional enterprise study reveal that 96% of UAE business leaders lack complete visibility into their software and infrastructure dependencies across external vendors and AI models. Another 74% struggle to adhere to cross-border data sovereignty and regulatory residency mandates.

“As organizations moved rapidly to the cloud, many prioritized speed and scale, assuming security controls could be layered on later,” said Rajeev Nair, Senior Vice President of Special Projects at digital transformation firm Core42. Nair cited unmanaged API keys, excessive administrative privileges, and weak threat triage as the three recurring infrastructure errors exposing Gulf enterprises.
A parallel vulnerability lies in how organizations conceptualize cloud storage, according to Fady Richmany, Corporate Vice President and General Manager for Emerging Markets at data resilience firm Commvault. While enterprise cloud migration is near-universal across Dubai and Abu Dhabi, many management teams incorrectly assume that a cloud provider’s uptime guarantees the safety and restorability of proprietary assets.
“Cloud providers ensure their platforms remain online, but safeguarding and restoring data, configurations, identities, and core workloads rests entirely with the business,” Richmany noted. Research by Absolute Security indicates that recovering operational capacity after a cyberattack takes organizations an average of 4.5 days, exposing enterprises to prolonged financial and operational paralysis.
Targeted strikes are concentrated across financial institutions, healthcare networks, logistics chains, and critical national infrastructure, explained Salah Suleiman, Managing Director for the South Gulf region at TrendAI.
“The more deeply connected an enterprise is to core infrastructure and economic systems, the higher its value to hostile actors,” Suleiman said. “Assessing risk requires evaluating systemic blast radius rather than just transaction volume. Defenses built for this operating environment will quickly degrade by 2027 if they do not dynamically evolve alongside automated threat vectors.”
To counter these vulnerabilities, security leaders advise corporate boards to institute isolated, air-gapped recovery partitions as a default safeguard, audit digital credentials for both human staff and autonomous software bots, and routinely rehearse recovery protocols in secure cleanroom sandboxes.